
Table of Contents
What Is Prevention For Security Vulnerabilities In Laravel?
Introduction
Laravel has robust, built-in security features, but like any software, apps built with it can still be vulnerable to specific attacks, and your application's security depends heavily on the skills of the development team.
Preventing security vulnerabilities in Laravel comes down to two things: using the framework's built-in protections (Blade escaping, Eloquent, CSRF tokens, secure hashing) and following security best practices such as input validation, HTTPS, and regular updates. Building resilient, trustworthy apps this way is part of the Laravel development services at Acquaint Softtech.
Common Vulnerabilities And How To Prevent Them
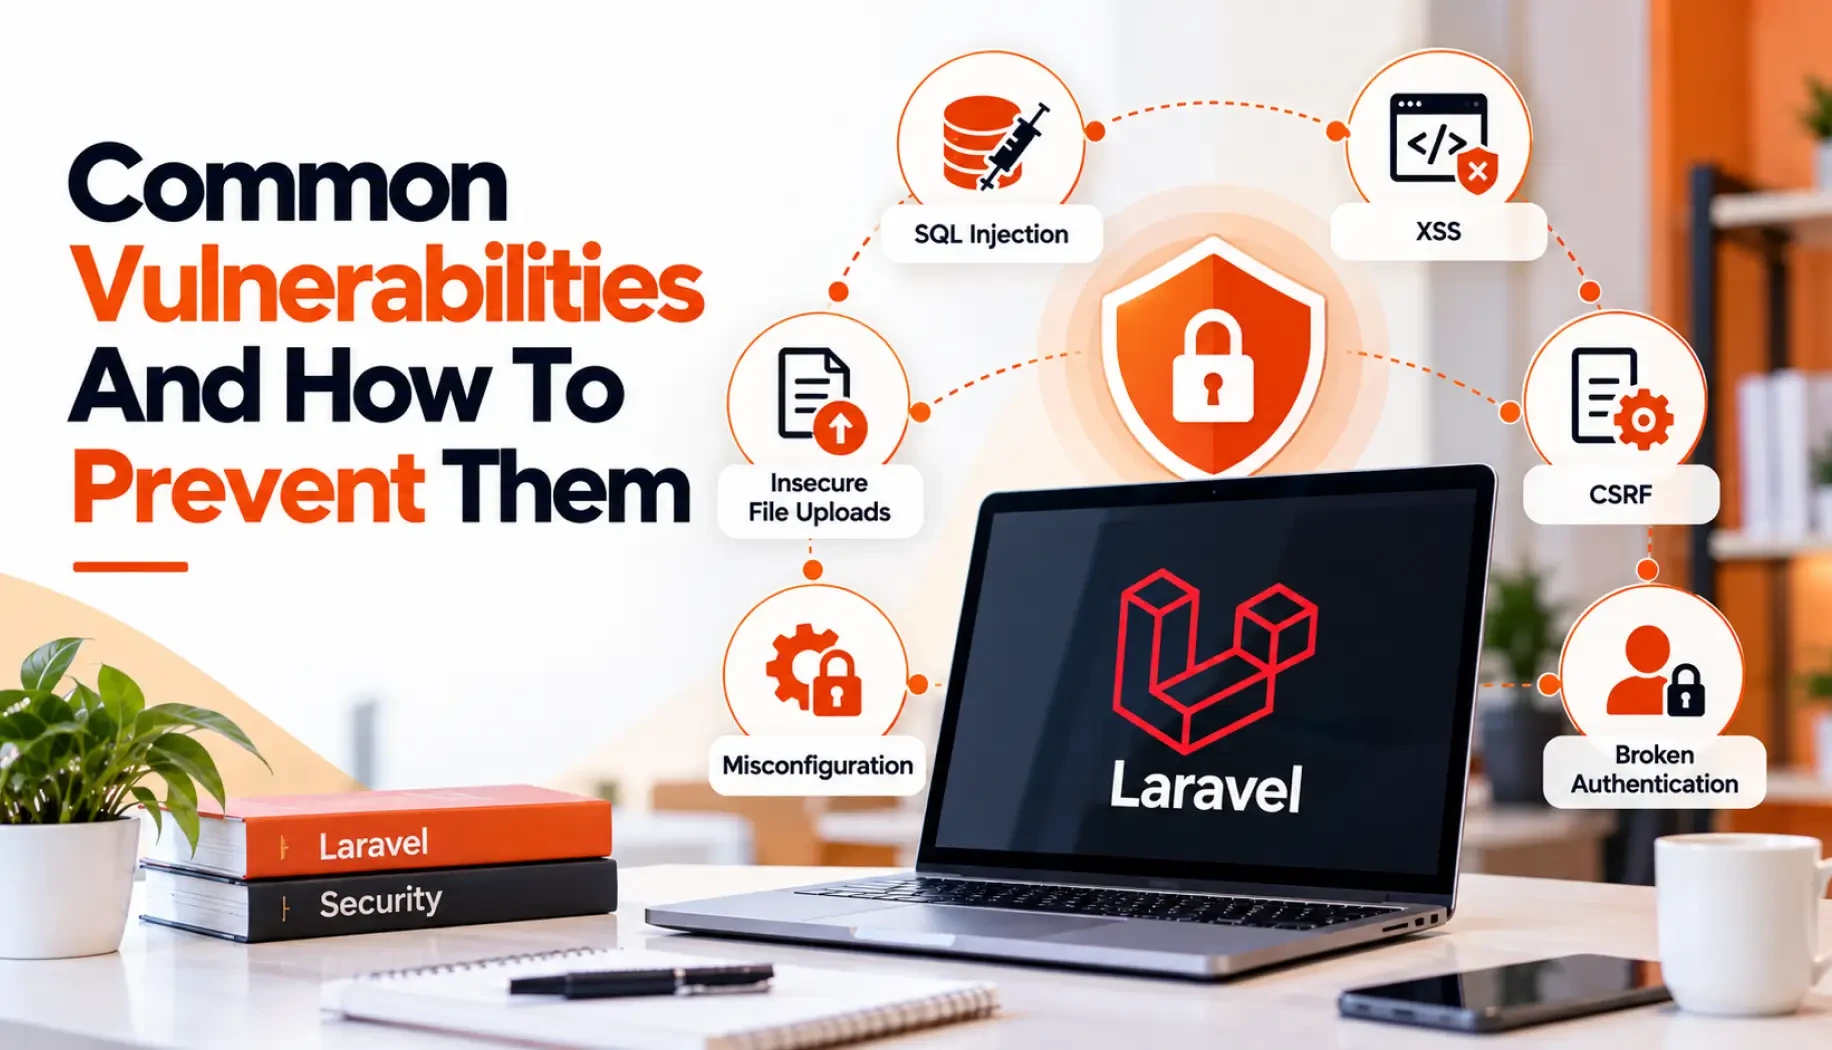
Here are the most common security vulnerabilities and how to prevent each one in Laravel. Strong input validation, covered in the official Laravel validation documentation, is the foundation of many of these defenses:
Vulnerability | How to prevent it in Laravel |
Cross-Site Scripting (XSS) | Blade auto-escapes output ({{ }}); validate input and set a Content Security Policy |
SQL Injection | Use Eloquent and the query builder (parameterized queries), never raw concatenation |
Cross-Site Request Forgery (CSRF) | Keep the @csrf token on all forms; the VerifyCsrfToken middleware checks it |
Insecure Direct Object References (IDOR) | Enforce authorization with gates and policies, not just hidden IDs |
Auth and session issues | Use Laravel auth, strong hashing, 2FA, and regenerate sessions on login |
Sensitive data exposure | Encrypt secrets, keep APP_DEBUG=false, and never log passwords or keys |
Unvalidated redirects | Validate and whitelist any user-supplied redirect URLs |
Vulnerable dependencies | Update Laravel, PHP, and packages, and run composer audit regularly |
Laravel's Built-In Protections
Laravel prevents many of these threats by default, which is a big part of why it is considered secure. Blade automatically escapes output to block XSS, Eloquent and the query builder use parameterized queries to stop SQL injection, the VerifyCsrfToken middleware guards every form against CSRF, and passwords are hashed with bcrypt or Argon2id.
Laravel also encrypts cookies, signs sessions, and provides an easy Crypt facade for encrypting sensitive data. The catch is that these only protect you when you use them; raw SQL, disabled escaping, or excluded CSRF routes reopen the door. That is why they matter most in custom Laravel development at Acquaint Softtech, where hand-written code is easier to get wrong.
Security Best Practices
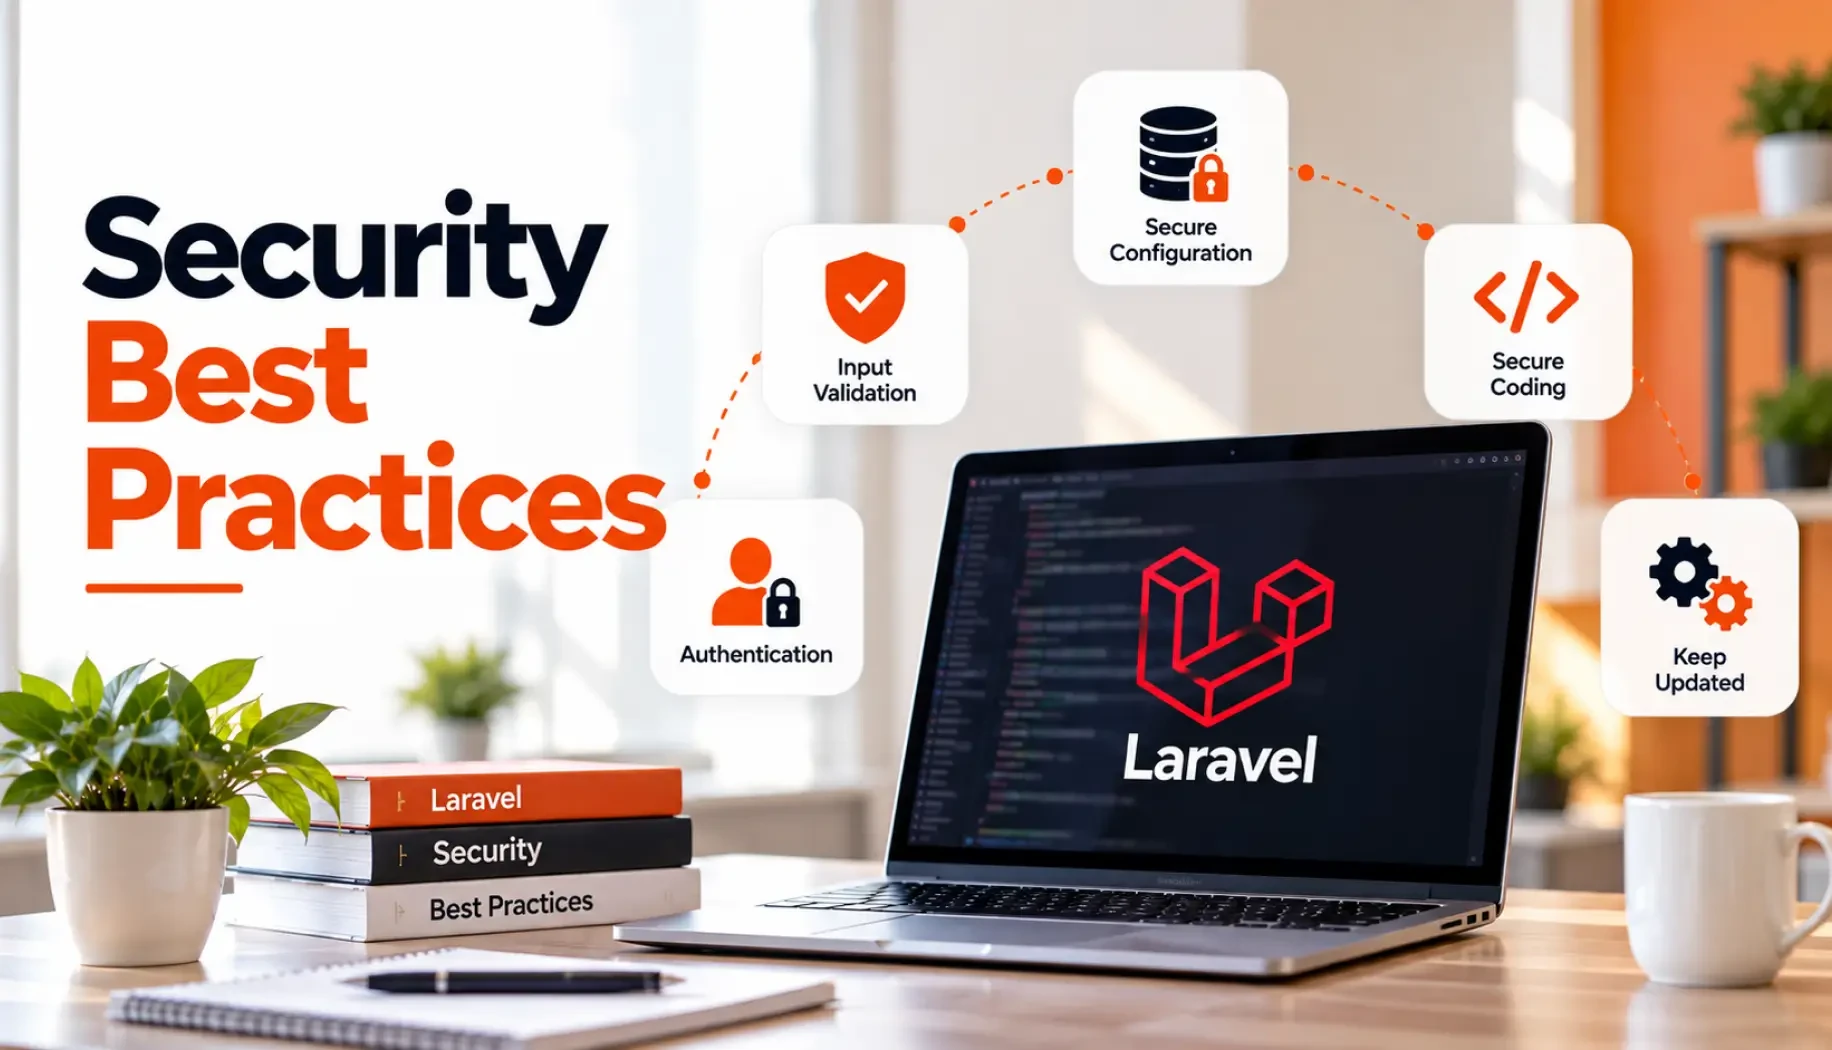
On top of the built-in defenses, follow these best practices:
Keep everything updated: update Laravel, PHP, and packages to patch known vulnerabilities.
Use HTTPS: apply SSL/TLS so data between client and server is encrypted in transit.
Validate and secure input: sanitize all user input, and validate and safely store file uploads.
Use auth and authorization: rely on Laravel's authentication, strong hashing, and gates and policies for access control.
Harden responses: configure error handling to avoid leaking system details, and add security headers like CSP and X-Frame-Options.
Audit and monitor: use logging and tools like Telescope, plus external scanners such as the Laravel Security Checker.
These practices are essential in large Laravel enterprise development.
Not Sure If Your Laravel App Is Secure?
Acquaint Softtech audits Laravel apps for vulnerabilities and hardens them against real threats. Book a free 30-minute consultation, no sales pitch, just honest advice.
Keeping Dependencies And Versions Patched
Most breaches exploit known, already-patched flaws, so keeping dependencies current is one of the highest-impact defenses. Run composer audit to flag vulnerable packages, keep the number of third-party dependencies lean (each one is extra risk), and stay on a supported Laravel and PHP version so you keep receiving security fixes. Running an app on an end-of-life version is a common, avoidable risk, and moving to a supported release is exactly the work that Laravel upgrade services from Acquaint Softtech handle.
Monitoring And Auditing
Security is ongoing, not a one-time setup. Monitor logs and login activity, review dependencies regularly, and run periodic security scans or penetration tests to catch new issues early. This continuous vigilance is part of Laravel maintenance and support at Acquaint Softtech.
Is Laravel Secure, And Does It Stop SQL Injection?
Is Laravel secure? Yes, it is one of the more secure PHP frameworks, with strong defaults. Does it prevent SQL injection automatically? Largely, if you use Eloquent or bound queries rather than raw SQL.
What are the most common vulnerabilities? The OWASP Top 10: XSS, injection, broken access control, and misconfiguration. Structuring defenses against all of these is the focus of a security blueprint for enterprise Laravel applications.
Building A Real Security Strategy
The gap between a hobby-grade and a production-grade setup is real, and it shows up under attack, as explored in novice vs professional Laravel security strategy.
Preventing Vulnerabilities With A Team
Preventing vulnerabilities takes both Laravel knowledge and a security mindset; one overlooked input or outdated package can undo the rest. If you want an audit or a hardened build, you can hire Laravel developers from Acquaint Softtech, an Official Laravel Partner and ISO 27001-certified company, to find and fix security gaps and keep your application resilient.
To Sum Up
Securing a Laravel application requires a varied approach, combining Laravel's built-in features with industry best practices. By staying updated, enforcing strict validation, and leveraging Laravel's robust security offerings, developers can significantly reduce the risk of vulnerabilities.
Remember, security is an ongoing process that requires vigilance, regular updates, and a proactive stance toward threats, so follow best practices like input validation, output escaping, parameterized queries, authentication, authorization, and encryption, and keep refining your security to safeguard your application against evolving digital threats.
India (Head Office)
203/204, Shapath-II, Near Silver Leaf Hotel, Opp. Rajpath Club, SG Highway, Ahmedabad-380054, Gujarat
USA
7838 Camino Cielo St, Highland, CA 92346
UK
The Powerhouse, 21 Woodthorpe Road, Ashford, England, TW15 2RP
New Zealand
42 Exler Place, Avondale, Auckland 0600, New Zealand
Canada
141 Skyview Bay NE , Calgary, Alberta, T3N 2K6