

Table of Contents
What Is SQL Injection Protection In Laravel?
Introduction
SQL injection protection in Laravel is a built-in security mechanism that ensures user-supplied data is treated strictly as literal data, not executable database code. Out of the box, Laravel automatically protects your application against SQL injection attacks when you use its standard database tools, the Eloquent ORM and the Fluent Query Builder.
Like any software, security is vital for Laravel apps, and while Laravel is a highly secure framework, it can still be vulnerable if optimal coding practices are not followed. Building applications that protect against SQL injection is central to the secure Laravel development services at Acquaint Softtech.
What Is SQL Injection?
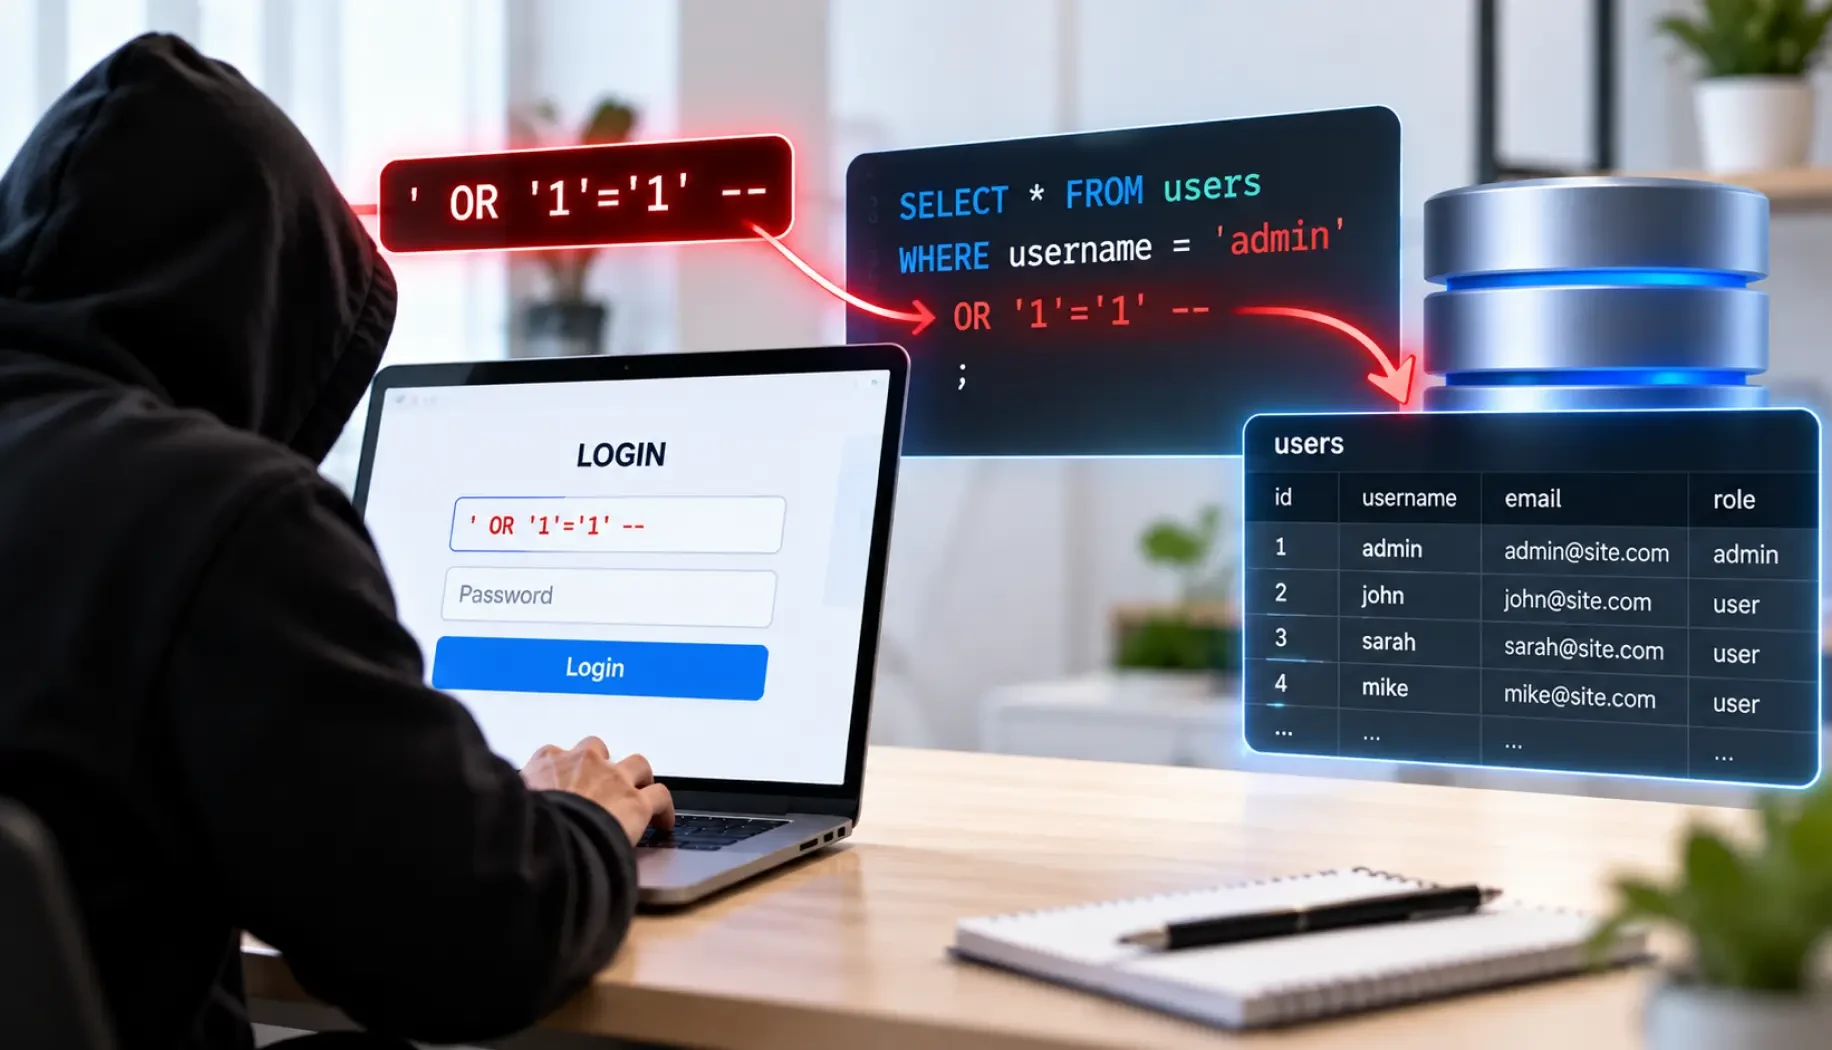
SQL injection is a web security vulnerability in which an attacker can manipulate the SQL queries executed by a web application's database. It occurs when untrusted user input is incorrectly filtered or not properly sanitized before being used in SQL queries. Here is how it typically works:
Injection point: an attacker identifies a form field, URL parameter, or other input that interacts directly with the database.
Malicious input: the attacker submits specially crafted input as part of that field, typically SQL code snippets.
Injection execution: if the app fails to sanitize the input, the injected SQL is concatenated with the original query and executed by the database server.
Unauthorized access: depending on the injected code, the attacker may bypass authentication, retrieve sensitive data, modify records, or run administrative commands.
For example, in a login query SELECT * FROM users WHERE email = '$email' AND password = '$password', an attacker entering ' OR '1'='1 as the password makes the condition always true, returning all rows and bypassing the check.
How Laravel Protects You Under The Hood
Laravel achieves this automatic protection primarily through PDO parameter binding, also called prepared statements. When you write a query with Eloquent or the Query Builder, Laravel separates the SQL query structure from the actual user data.
The database server, whether MySQL, PostgreSQL, or Oracle, compiles the SQL structure before the user input is inserted, so when the input is finally bound to the parameters, the database treats it entirely as a harmless string or value, rendering any injected SQL commands completely inert. The official Laravel query builder documentation explains the binding in detail.
Safe Vs Unsafe Queries
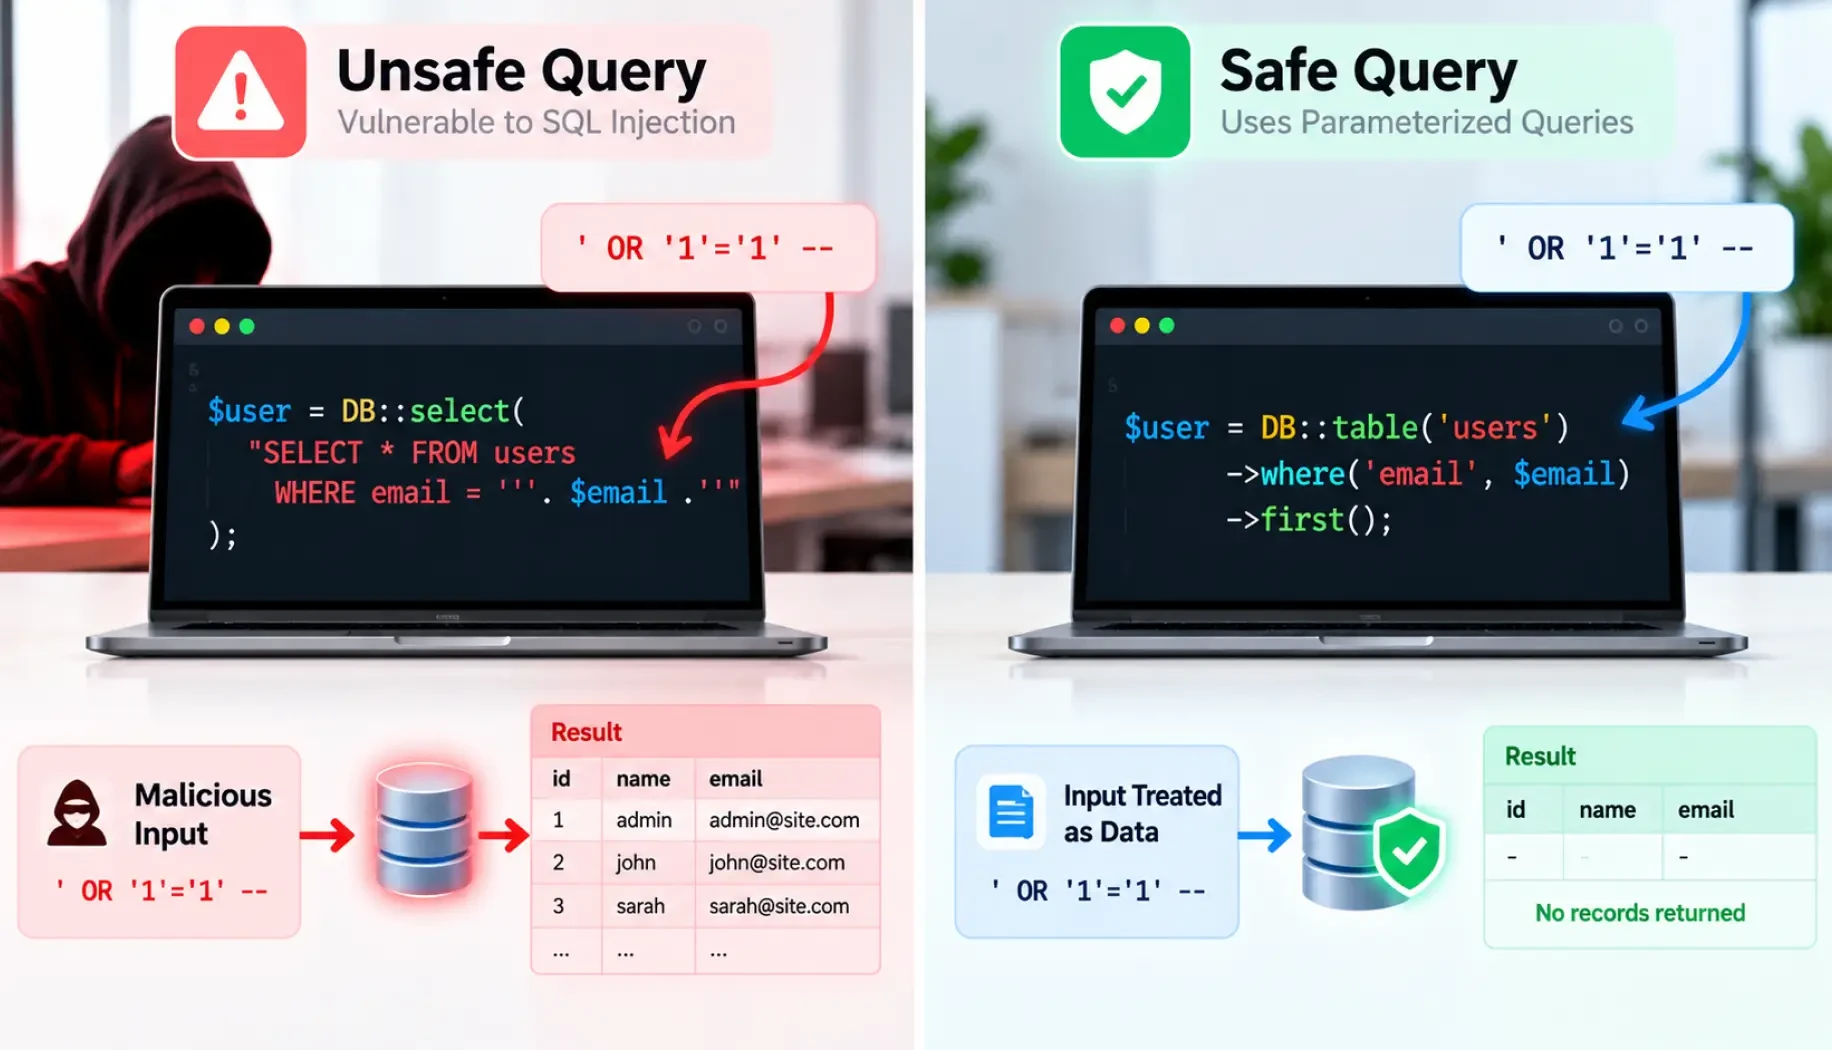
The safest approach is Laravel's ORM and Query Builder; danger comes from concatenating input into raw SQL. Here is the comparison:
Query type | Example | Status |
Standard Eloquent | User::where('email', $input)->first(); | Secure (auto-bound via PDO) |
Query Builder | DB::table('users')->where('id', $input)->get(); | Secure (auto-parameterized) |
Raw SQL with bindings | DB::select("... WHERE status = ?", [$status]); | Secure (? placeholders) |
Raw SQL concatenation | DB::select("... = '" . $status . "'"); | Vulnerable (bypasses escaping) |
Getting raw queries right when they are unavoidable is part of secure custom Laravel development at Acquaint Softtech.
Best Practices To Prevent It
Laravel's Eloquent ORM and Fluent Query Builder are the first lines of defence against SQL injection, automatically using parameter binding so user input is treated as data, not executable code, and escaping dangerous characters. The built-in protections include:
Query Builder: a fluent interface for building database queries that automatically escapes user input.
Eloquent ORM: a higher-level abstraction for database interaction that automatically handles parameter binding.
Parameter binding: binds user input to query parameters so input is treated as data rather than executable code.
Validation and sanitisation: validates and cleans user input before it is used in any query.
Laravel also allows raw SQL for complex queries, and there it is crucial to use parameter binding; for example, DB::select('SELECT * FROM users WHERE username =:username', ['username' => $username]), where:username is a placeholder that Laravel safely binds. Broader measures are covered in security practices for Laravel web applications.
When Can Laravel Apps Become Vulnerable?
Laravel is not a silver bullet; it protects you only if you use its features correctly. Vulnerabilities usually arise when developers accidentally bypass its native protections:
Using unsafe raw methods: using whereRaw, selectRaw, orderByRaw, or DB::raw() and directly concatenating variables into the string instead of using array bindings.
Relying solely on input validation: Form Requests and validation rules keep data clean, but validation alone cannot block complex payloads mixed into raw queries.
Leaving debug mode on in production: APP_DEBUG=true exposes detailed database errors and query traces that give attackers the clues they need for blind SQL injection.
These gaps are most dangerous at input-heavy Laravel API development endpoints.
Core Best Practices And Testing For Vulnerabilities
A few core practices keep you safe:
Stick to the ORM: lean heavily on Eloquent methods like where, find, and update for database communication.
Always bind raw parameters: if you must use a raw method, pass user input inside an array as the second argument, for example, DB::select("... WHERE id = ?", [$id]).
Turn off debugging: ensure APP_DEBUG=false in production environments.
SQL injection sits high on the OWASP Top 10 for Laravel and every framework, so beyond code, teams run a Laravel security checker (such as composer audit for known package vulnerabilities) and penetration testing, where testers probe inputs with fuzzing wordlists to find injection points. Layering these into a full plan is what the security blueprint for enterprise Laravel applications covers.
Is Your Laravel App Safe From SQL Injection?
Acquaint Softtech audits and hardens Laravel applications against SQL injection and other risks. Book a free 30-minute consultation, no sales pitch, just honest advice.
Is SQL Injection Still Used, And What Damage Can It Cause?
Yes, SQL injection is still one of the most common and dangerous web attacks, which is why it remains on the OWASP Top 10. The damage can be severe: attackers can bypass authentication, steal or leak sensitive data, modify or delete records, corrupt the database, or gain administrative control of the system. For high-value systems, this makes injection protection a first-order concern in Laravel enterprise development at Acquaint Softtech.
How To Prevent SQL Injection In PHP?
In plain PHP, you prevent SQL injection with PDO or MySQLi prepared statements and parameter binding, never concatenating user input into query strings. Laravel does this for you through Eloquent and the Query Builder. Keeping PHP and Laravel patched to the latest version also closes known holes, which is part of ongoing Laravel maintenance and support from Acquaint Softtech.
What Is SQL Injection Protection?
SQL injection protection is any technique that stops user input from changing the meaning of a database query. The core method is parameterised (prepared) queries, where input is bound as data rather than inserted into the SQL text, combined with input validation, least-privilege database accounts, and hidden error messages so attackers get no useful feedback.
Securing Your App With A Laravel Team
Preventing SQL injection is mostly about discipline: using the ORM by default, binding every raw parameter, validating input, turning off debug in production, and testing regularly. That discipline is easy to slip on under a deadline, and a single concatenated raw query can undo it. A secure application also needs the surrounding measures, patched dependencies, least-privilege database users, and periodic security reviews.
If you want that handled end to end, you can hire Laravel developers from Acquaint Softtech, an Official Laravel Partner and ISO 27001-certified company, whose engineers write injection-safe queries by default and review the codebase for the raw-SQL mistakes that put data at risk, so your users' data stays protected as the application grows.
To Wrap Up
SQL injection is a prevalent security vulnerability that lets an attacker interfere with an application's database queries, and it can be used to steal data, corrupt databases, or even gain administrative access to a system. When used correctly, Laravel's built-in security features provide robust protection against it, so by understanding and utilizing these features, developers can build secure applications that protect user data and maintain the integrity of their databases. Security is a continuous process, and staying informed about the latest practices is essential for safeguarding your applications against evolving threats.
India (Head Office)
203/204, Shapath-II, Near Silver Leaf Hotel, Opp. Rajpath Club, SG Highway, Ahmedabad-380054, Gujarat
USA
7838 Camino Cielo St, Highland, CA 92346
UK
The Powerhouse, 21 Woodthorpe Road, Ashford, England, TW15 2RP
New Zealand
42 Exler Place, Avondale, Auckland 0600, New Zealand
Canada
141 Skyview Bay NE , Calgary, Alberta, T3N 2K6