

Table of Contents
What Is CSRF Protection In Laravel?
Introduction
CSRF (Cross-Site Request Forgery) protection in Laravel is a built-in security feature that stops attackers from tricking a logged-in user's browser into sending unwanted requests, like changing an email or password, without their consent.
Laravel handles this with a token-based approach: it generates a unique CSRF token for each user session and requires that token in every POST, PUT, PATCH, or DELETE request, then verifies it automatically against the one in the session. Building secure applications like this is part of the Laravel development services at Acquaint Softtech.
How CSRF Works
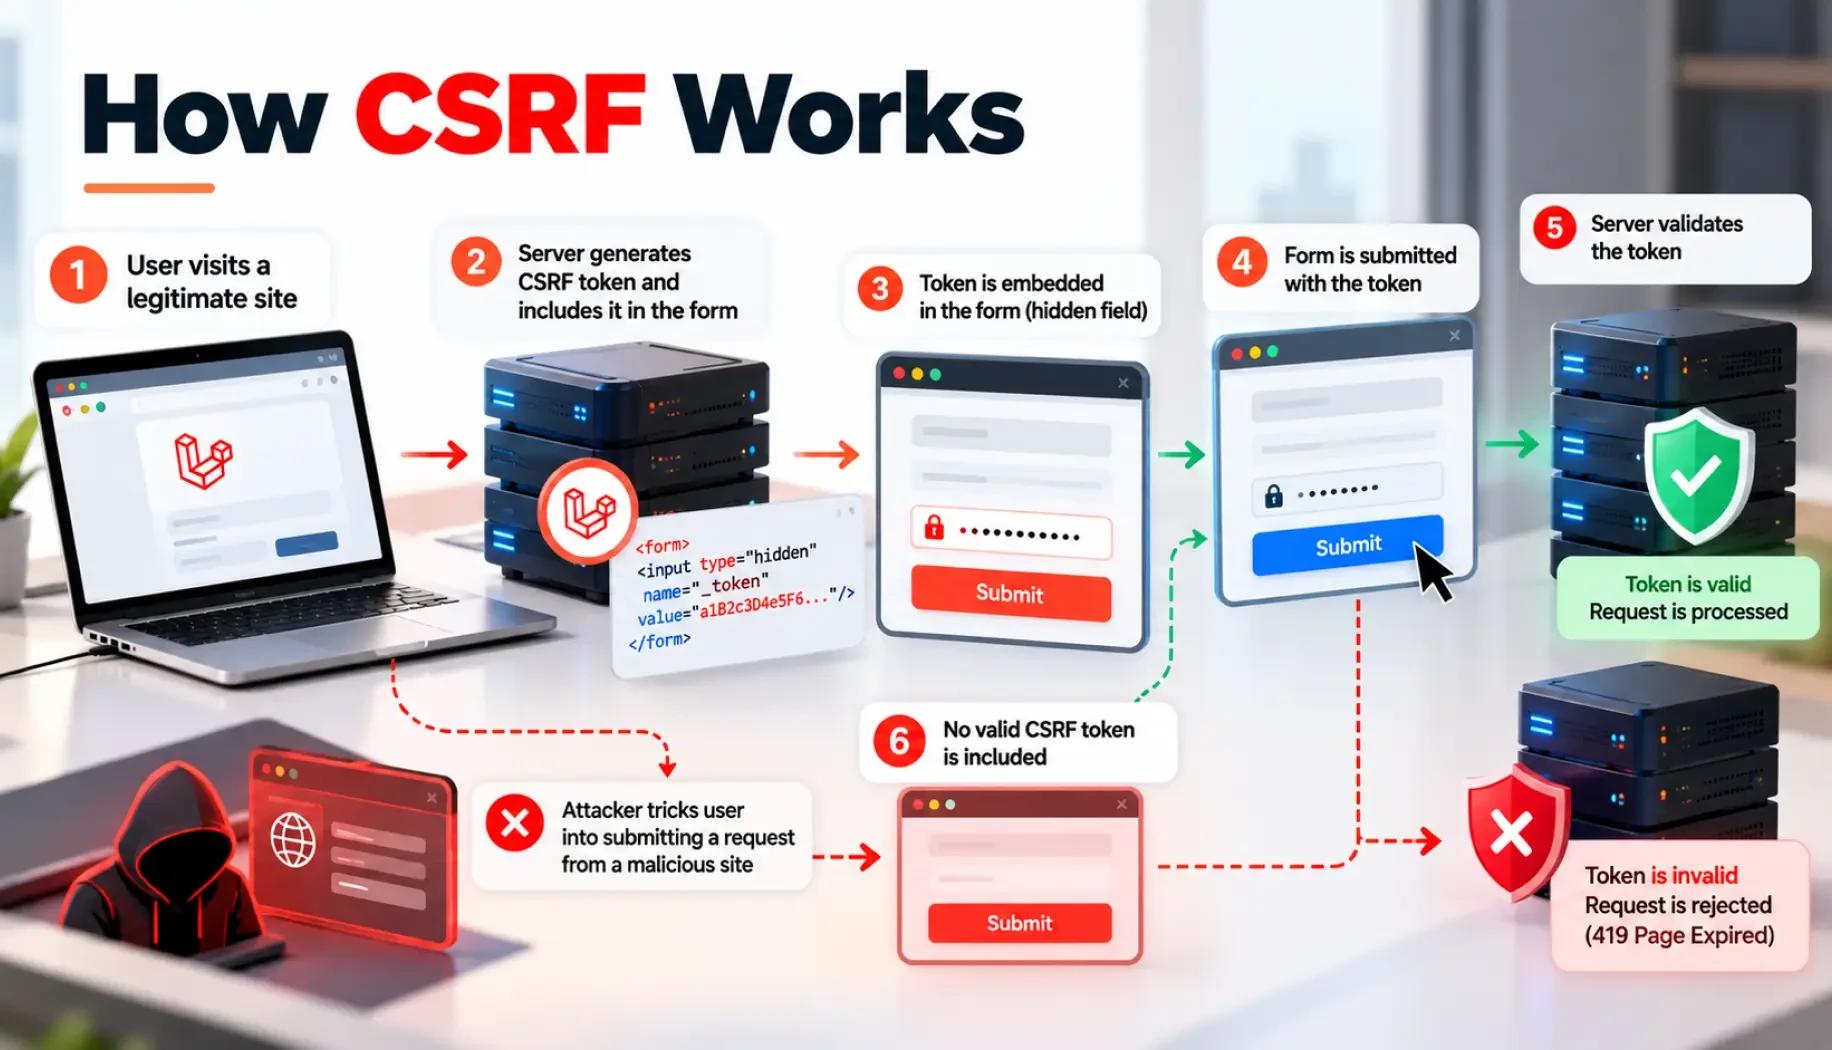
CSRF attacks exploit the trust a site places in the user's browser: if a user is logged in, a malicious site can send a request to the app on their behalf and perform unwanted actions without their knowledge.
Laravel's protection is straightforward: you add the token to a form with the @csrf Blade directive (or the csrf_field() and csrf_token() functions), and the VerifyCsrfToken middleware, included in the web middleware group by default, verifies that the token in the request matches the one stored in the session.
That makes secure form handling standard in Laravel web application development at Acquaint Softtech.
How To Add The CSRF Token
Laravel generates a CSRF token for each active session, and how you include it depends on the context, all covered in the official Laravel CSRF documentation:
Context | How to include or check the CSRF token |
Blade forms | The @csrf directive (or csrf_field()) adds a hidden token input to the form |
Manual or inline | csrf_token() returns the raw token value to place wherever you need it |
AJAX requests | Store the token in a meta tag and send it as an X-CSRF-TOKEN header |
Validation | The VerifyCsrfToken middleware checks the token; a mismatch returns HTTP 419 |
Excluded routes | List URIs, such as external webhook APIs, to skip the CSRF check |
Token Validation And Excluding Routes
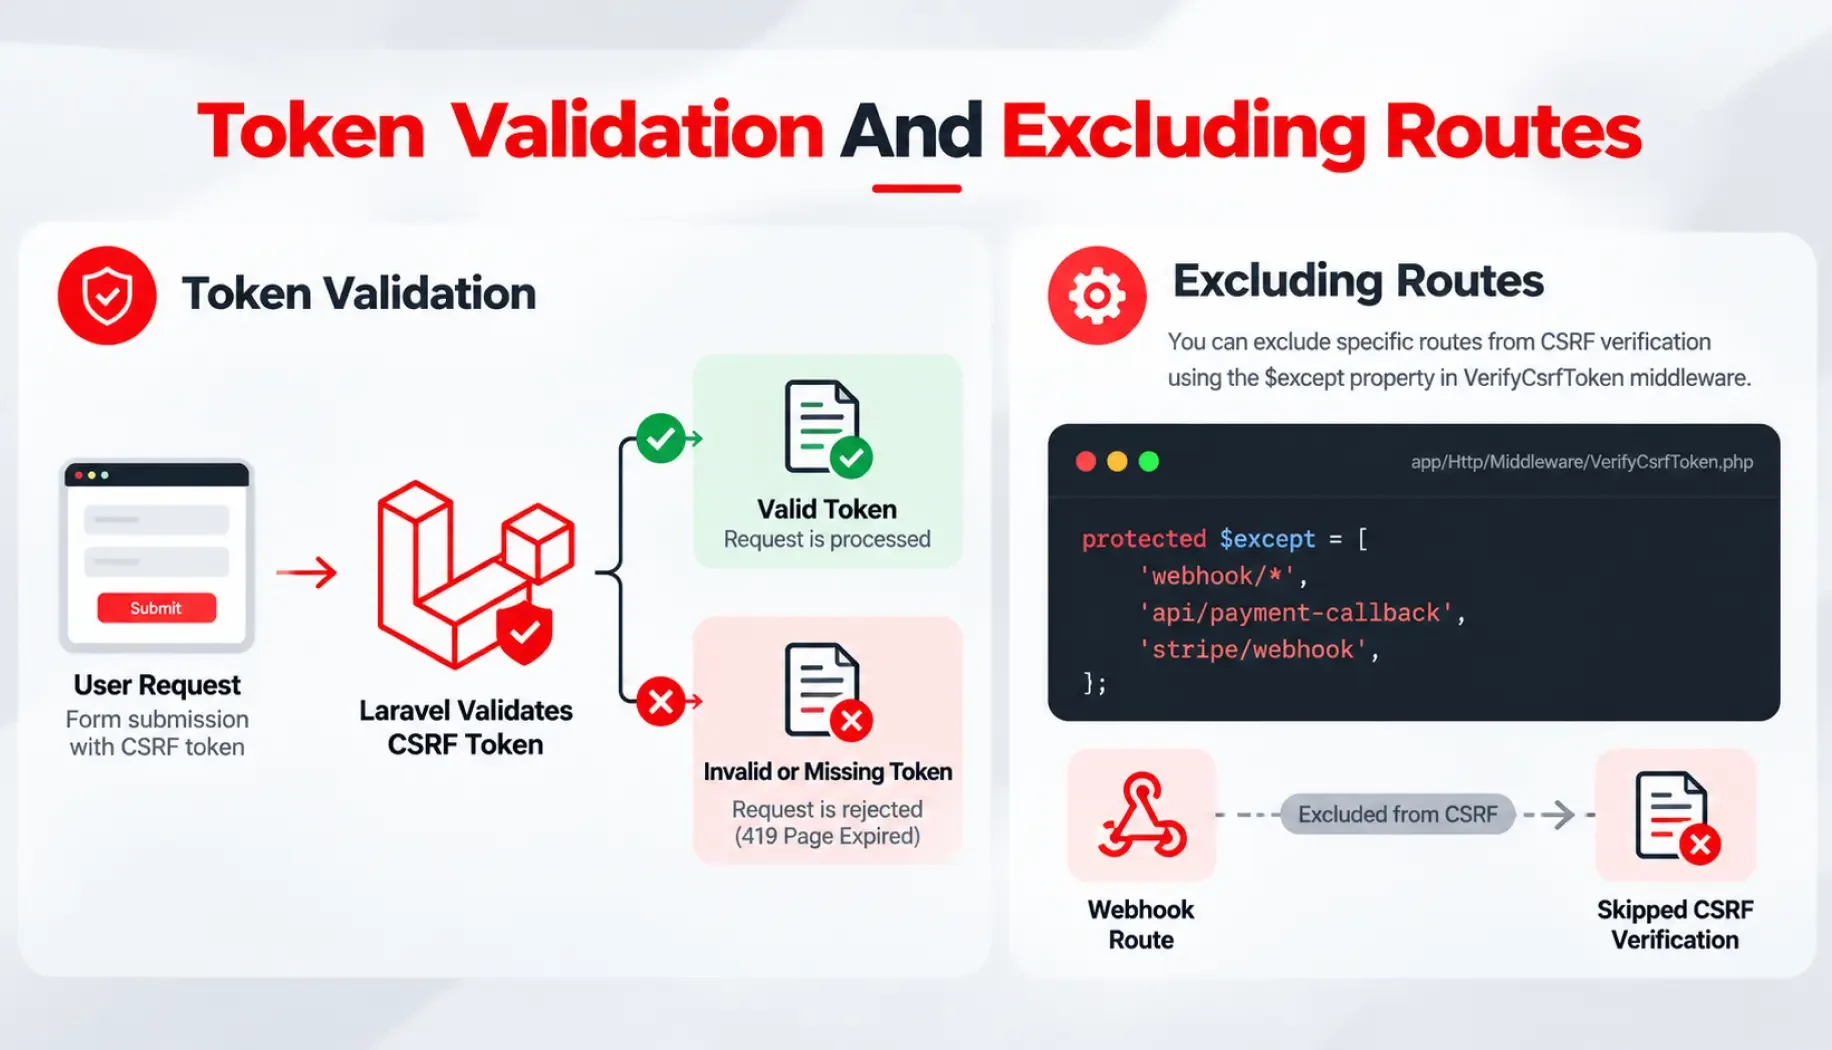
When a request arrives, Laravel checks the token automatically, and if it is missing or invalid, it rejects the request with a 419 (session expired) status. You can also exclude certain routes from CSRF protection, for example, APIs that expect external requests, by listing those URIs (in the VerifyCsrfToken middleware on Laravel 10 and older, or in bootstrap/app.php on Laravel 11 and newer). CSRF sits within a broader set of security practices for Laravel web applications.
Lock Down Your Laravel App Against CSRF And More
Acquaint Softtech builds and reviews secure request handling, CSRF, auth, and validation across your Laravel app. Book a free 30-minute consultation, no sales pitch, just honest advice.
Do APIs Need CSRF Protection?
A common question is whether APIs need CSRF. Token-based APIs (using Sanctum or Passport) do not rely on session cookies, so they are not vulnerable to CSRF and typically skip it, while cookie-based single-page apps still need it. Getting this distinction right is part of Laravel API development at Acquaint Softtech.
CSRF And External Integrations
External services like payment gateways send POST webhooks that cannot carry your CSRF token, so those specific routes are excluded from the CSRF check (and secured another way, such as signature verification). Wiring up those integrations safely is part of Laravel integration services at Acquaint Softtech.
Common Questions On CSRF Protection
What is the 419 error in Laravel? It means the CSRF token was missing or expired, often after a form sits open too long, so refreshing and resubmitting usually fixes it. How do I disable CSRF for a route? Exclude that URI rather than turning protection off globally.
And what is a CSRF token? A unique, per-session value Laravel uses to confirm a request really came from your app. Keeping these protections correct over time is part of Laravel maintenance and support.
One Layer Of A Bigger Security Picture
CSRF is one layer among many; it works alongside authentication, input validation, and XSS protection to keep an app safe, as covered in 5 security practices to consider for Laravel.
Getting Security Right With A Team
CSRF protection is largely automatic in Laravel, but using it correctly- keeping @csrf on every form, handling AJAX headers, and excluding only the routes that truly need it, still takes care, because a wrong exclusion opens a hole.
If you want that done right, you can hire Laravel developers from Acquaint Softtech, an Official Laravel Partner and ISO 27001-certified company, to build and review secure request handling across your application.
To Sum Up
CSRF protection is a critical security measure that helps safeguard user data and actions from being misused. Laravel provides a robust, easy-to-use CSRF protection system that, when properly implemented, adds a necessary layer of security to web applications, making them safer for users. It is one clear example of Laravel's commitment to security and ease of use, giving developers the tools to build secure applications efficiently.
India (Head Office)
203/204, Shapath-II, Near Silver Leaf Hotel, Opp. Rajpath Club, SG Highway, Ahmedabad-380054, Gujarat
USA
7838 Camino Cielo St, Highland, CA 92346
UK
The Powerhouse, 21 Woodthorpe Road, Ashford, England, TW15 2RP
New Zealand
42 Exler Place, Avondale, Auckland 0600, New Zealand
Canada
141 Skyview Bay NE , Calgary, Alberta, T3N 2K6