

Table of Contents
What is Authorization in Laravel?
Introduction
Authorization in Laravel is the process of deciding what an authenticated user is allowed to do, whether they can perform a specific action or access a particular resource.
It works alongside authentication: authentication verifies who a user is, while authorization grants them a predefined level of access based on their role, permissions, or rules. Building secure, role-aware applications is part of the Laravel development services at Acquaint Softtech.
Authentication Vs Authorization
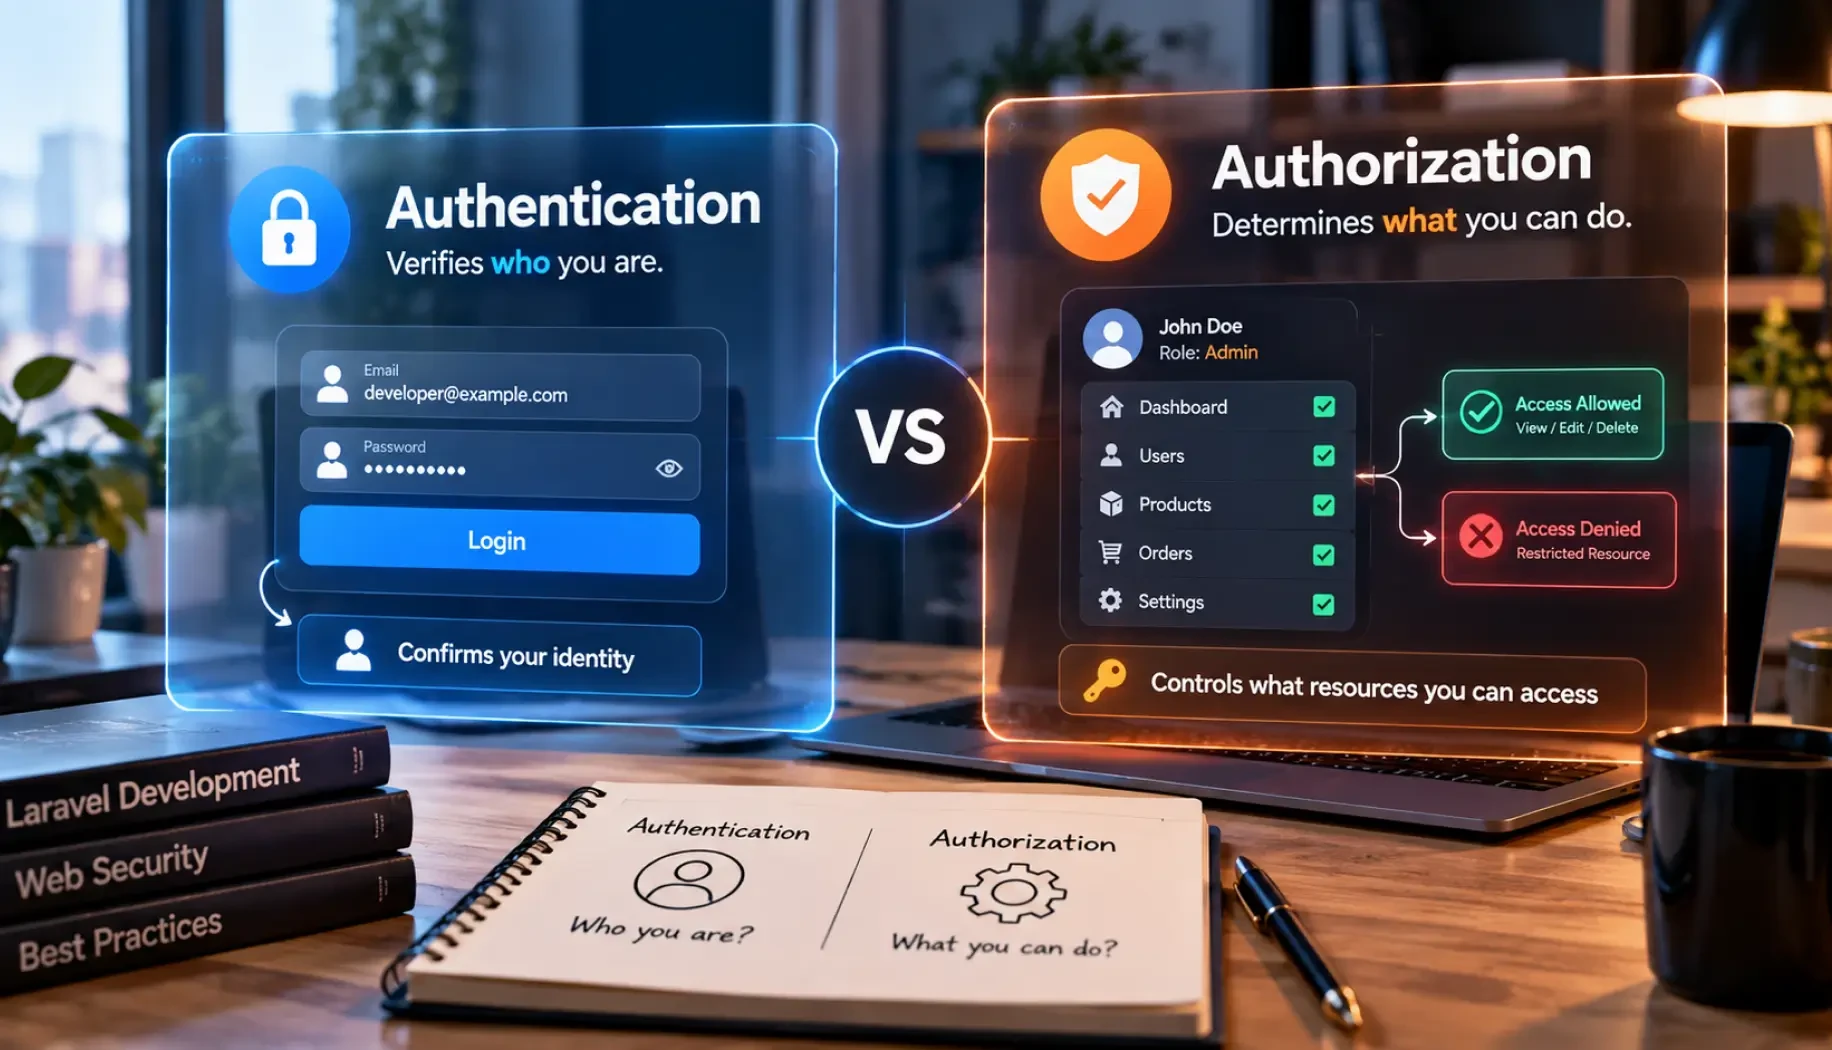
The two are easy to confuse. Think of your home: authentication is like showing an ID to get through the front door; if your credentials are right, you are let in. Authorization is the next layer: once inside, it decides which rooms you can enter and which things (the computer, the safe) you can use.
In a web app, authentication verifies credentials like a username and password, and the authorization system then defines what actions and resources that user can access based on their role, permissions, or other rules. Getting these access rules right is part of custom Laravel development at Acquaint Softtech.
Gates Vs Policies
Laravel gives you two main tools for authorization, gates and policies, both explained in the official Laravel authorization documentation:
Aspect | Gates | Policies |
What it is | A closure-based check for a single ability | A class that groups authorization rules for one model |
Best for | Simple, one-off checks not tied to a model | Model-specific rules (view, update, delete a Post) |
Defined with | Gate::define() in a service provider | php artisan make:policy, one method per action |
Checked with | Gate::allows() or @can | can(), authorize(), or @can |
Gates And Policies Explained
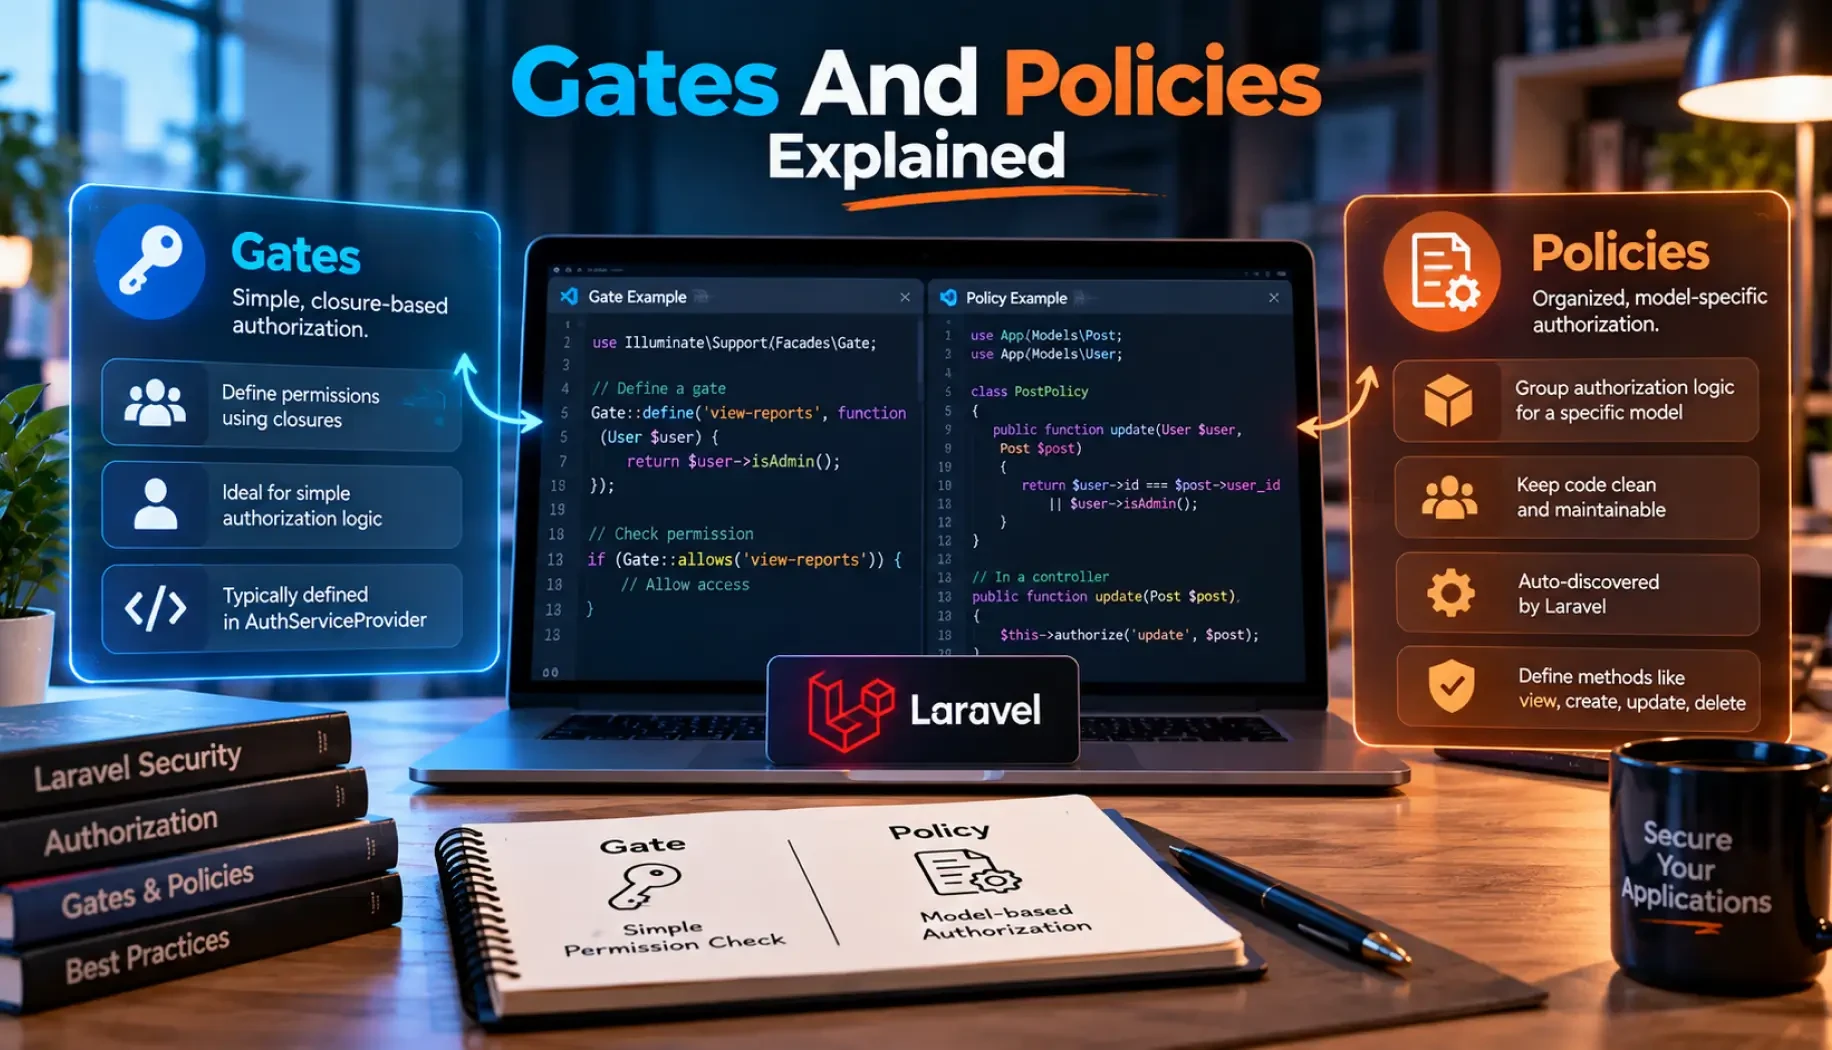
Gates let you create your own authorization rules based on any criteria, a simple checkpoint for whether a user can perform a task; you define one with Gate::define() and check it with Gate::allows().
Policies offer a higher level of abstraction, encapsulating the authorization logic for a particular model or resource, usually an Eloquent model; you generate one with php artisan make:policy and register it with Gate::policy().
Together, they keep authorization logic organized and reusable, which matters most on large systems with many roles, common in Laravel enterprise development at Acquaint Softtech.
Lock Down Access In Your Laravel App
Acquaint Softtech designs clear gates, policies, and roles so every action is properly guarded. Book a free 30-minute consultation, no sales pitch, just honest advice.
Checking Permissions
You check authorization in a few clean ways: $user->can('update', $post) or authorize('update', $post) in a controller, the @can and @cannot directives in Blade to show or hide UI, and the can middleware to protect routes. For APIs, Sanctum token abilities add scope-based control on top, which fits naturally into Laravel API development.
Role-Based Access Control (RBAC)
For apps with many roles, teams often add role-based access control, usually with the popular Spatie laravel-permission package, to manage roles and permissions cleanly on top of gates and policies. Structuring this well is part of a wider security blueprint for enterprise Laravel applications.
Common Questions On Authorization
What is the difference between a gate and a policy? A gate is a standalone check, while a policy groups a model's rules in one class. How do I check permissions in Laravel? With can(), authorize(), the @can directive, or the can middleware.
And is authorization the same as authentication? No, authentication is who you are; authorization is what you are allowed to do. Keeping these rules correct as an app grows is part of Laravel maintenance and support at Acquaint Softtech.
Access Control And Security Strategy
Done poorly, access control leaves holes; done well, it is invisible and airtight a difference explored in novice vs professional Laravel security strategy.
Getting Authorization Right With A Team
Authorization is easy to get subtly wrong; a missing policy check or an over-broad gate can expose data, and the mistakes rarely show up until someone finds them. If you want it done right, you can hire Laravel developers from Acquaint Softtech, an Official Laravel Partner and ISO 27001-certified company, to design clear, testable gates, policies, and roles that keep every action properly guarded.
Final Thoughts
In short, authorization in Laravel controls what an authenticated user can do, using gates for simple checks and policies for model-specific rules, with role-based permissions layered on when an app needs them. Combined with authentication, it lets you build robust, secure applications where every user sees and does exactly what they should, and nothing more.
India (Head Office)
203/204, Shapath-II, Near Silver Leaf Hotel, Opp. Rajpath Club, SG Highway, Ahmedabad-380054, Gujarat
USA
7838 Camino Cielo St, Highland, CA 92346
UK
The Powerhouse, 21 Woodthorpe Road, Ashford, England, TW15 2RP
New Zealand
42 Exler Place, Avondale, Auckland 0600, New Zealand
Canada
141 Skyview Bay NE , Calgary, Alberta, T3N 2K6